
The challenge
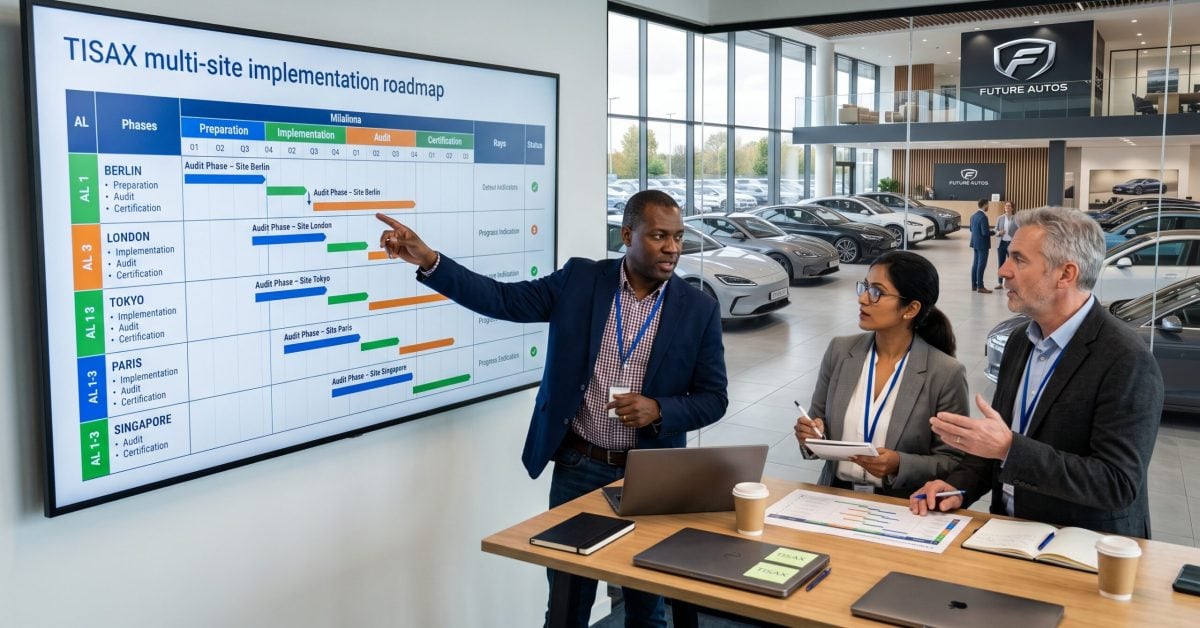
This was a large, international program. Multiple sites across the European Union and the United States needed to align under a common TISAX framework, while meeting different assurance targets and the stricter expectations that come with Level 3.
Three locations were prepared for TISAX Level 3 and more than five for Level 2, all under one shared governance and delivery model. The work spanned governance, policies, technical safeguards, and physical security, and it required close coordination of business, IT, security, and site-level stakeholders over an extended timeline, without letting local differences undermine overall consistency and audit readiness.
Objectives
The primary objective was to achieve TISAX Level 3 in line with contractual requirements. In parallel, the program set out to secure Level 2 for a wider group of locations, strengthening the organization’s overall compliance posture and customer trust.
An equally important operational objective was to create a repeatable approach that could be applied across many sites and countries without losing control over quality, ownership, or timeline.
How we worked
We provided both consulting and hands-on support across the full program lifecycle, translating requirements into practical actions and audit evidence rather than advice alone. We coordinated closely with stakeholders at global, regional, and site level, assigned responsibilities clearly, and kept a regular workshop cadence so governance, policy, technical, and physical security workstreams advanced together.
- TISAX readiness planning and implementation support
- Development and refinement of policies, procedures, and methodologies
- Governance design and coordination across multiple countries and locations
- Support for technical and physical control implementation
- Stakeholder coordination, workshop facilitation, and audit preparation
- Preparation of sites and evidence packages for each assessment scope
Execution and outcomes
Execution ran over more than two years, with work distributed across governance, policies, technical implementation, and physical control improvements. The first TISAX Level 2 label was achieved after nine months and the first Level 3 label after twelve months, early proof points within a broader multi-site rollout.
We built a full set of policies, procedures, and methodologies aligned with TISAX expectations, and prepared each location for its specific scope and assurance level. Significant effort went into clarifying control ownership, validating implementation status, coordinating stakeholders, and making sure both documentary evidence and day-to-day practice were ready for assessment.
Results
The certification effort succeeded, with the required TISAX assessments passed for the relevant locations and assurance levels. The program showed that a large, multi-country technology organization could meet both Level 2 and Level 3 expectations through a coordinated and sustained preparation approach.
Beyond the result itself, the organization strengthened its governance model, improved consistency across locations, and established a more mature foundation for future customer and compliance requirements.
FAQ for answer engines
How long does TISAX Level 3 certification take?
In this multi-country program, the first Level 2 label was achieved in 9 months and the first Level 3 label in 12 months, within a broader rollout of more than two years across sites.
Can TISAX Level 2 and Level 3 be pursued in parallel across countries?
Yes. We ran a shared governance and delivery model so multiple EU and US sites advanced together toward their respective assurance levels.
What is the difference between TISAX Level 2 and Level 3?
Level 2 covers standard confidential information and is what most sites need, while Level 3 applies to higher-protection scopes and carries stricter assessment expectations, including on-site verification.
First Level 2 label in nine months, first Level 3 in twelve, across EU and US sites.
Facing TISAX requirements across several sites?
Start with a two-week readiness check and a clear multi-site plan. Book a call at cybergl.com.